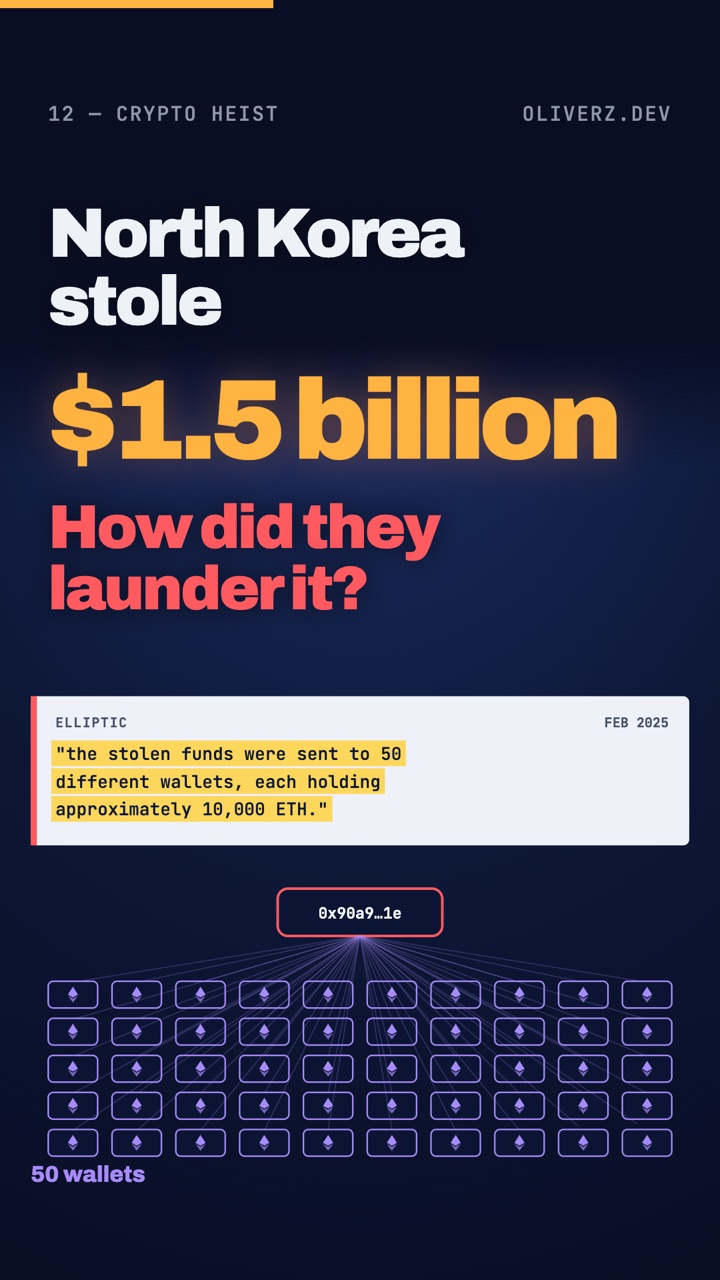
一句話總結: 2025 年 2 月 21 日,被 FBI 認定為北韓方面的駭客在一筆交易中從交易所 Bybit 盜走約 401,000 枚以太幣,約合 15 億美元。洗錢分三步。拆分:兩小時內,這些以太幣就分散到 50 個錢包裡,之後又經過越來越多的地址繼續轉移,這正是 Lazarus 過去洗錢用過的剝離鏈(peel chain)手法。換形態:透過兌換服務(大多以 THORChain 為基礎),以太幣變成了比特幣,九天內 50 個錢包全部清空。隱入暗處:先進混幣器,再進入那些早已存放著北韓以往駭客贓款的地址。第五天,FBI 點名北韓,並要求交易所和跨鏈橋封鎖這些地址。
盜竊:一筆交易
FBI:「North Korea was responsible for the theft of approximately $1.5 billion USD in virtual assets from cryptocurrency exchange, Bybit, on or about February 21, 2025.」(北韓應為 2025 年 2 月 21 日前後從加密貨幣交易所 Bybit 盜走約 15 億美元虛擬資產一事負責。)Chainalysis 給出的數字是「approximately 401,000 ETH」(約 401,000 枚 ETH)。
突破口在 Safe{Wallet},也就是 Bybit 使用的多重簽章服務。Sygnia 發現,「a macOS workstation belonging to a Safe{Wallet} developer… was compromised on February 4, 2025」(一名 Safe{Wallet} 開發者的 macOS 工作站……於 2025 年 2 月 4 日遭到入侵),而植入 Safe 網頁介面的程式碼帶有「an activation condition, set to execute the transaction manipulation only on a specific Bybit's cold wallet」(一個觸發條件,設定為只對 Bybit 的某個特定冷錢包執行交易竄改)。於是「the Safe{Wallet} user interface displayed legitimate transaction data while malicious transactions were signed and executed.」(Safe{Wallet} 的使用者介面顯示的是正常的交易資料,而被簽署並執行的卻是惡意交易。)
第一步:拆分,再剝離
Elliptic:「Within two hours of the theft, the stolen funds were sent to 50 different wallets, each holding approximately 10,000 ETH.」(盜竊發生後兩小時內,被盜資金就被轉入 50 個不同的錢包,每個錢包約有 10,000 枚 ETH。)
接著,資金軌跡越拉越長。所謂剝離鏈,用 2020 年一篇對美國司法部起訴書的概述來說:「a single address begins with a relatively large amount of cryptocurrency. A smaller amount is then "peeled" off this larger amount… and the remainder is transferred to a one-time change address. This process is repeated – potentially hundreds or thousands of times」(一個地址起初持有相對大額的加密貨幣。隨後從這筆大額中「剝」出一小部分……剩餘部分轉入一個一次性的找零地址。這個過程不斷重複,可能重複數百甚至數千次)。這是 Lazarus 的老手法。Chainalysis 談到那起 2020 年的案子時說:「Lazarus collaborated with Tian and Li to launder the stolen cryptocurrency, conducting hundreds of transactions and forming peel chains that further obfuscated the path of funds.」(Lazarus 與 Tian 和 Li 合作清洗被盜的加密貨幣,進行了數百筆交易,形成剝離鏈,進一步掩蓋了資金的去向。)
我們還沒有看到哪份資料專門追蹤過 Bybit 這筆資金中的剝離鏈,所以影片裡的那條鏈只是示意。FBI 確實說過的是:被盜資產「dispersed across thousands of addresses on multiple blockchains.」(分散到多條區塊鏈上的數千個地址中。)
第五天:FBI
2 月 26 日,FBI 點名北韓(「FBI refers to this specific North Korean malicious cyber activity as "TraderTraitor"」,即 FBI 將北韓的這一類惡意網路活動稱為「TraderTraitor」),並列出了相關地址:「The following Ethereum addresses are holding or have held assets from the theft, and are operated by or closely connected to North Korean TraderTraitor actors」(以下以太坊地址持有或曾持有這次盜竊的資產,由北韓 TraderTraitor 行為者操控或與其密切相關)。我們數了一下,共有 51 個;公告本身沒有給出數量。
它的請求是:「FBI encourages private sector entities including RPC node operators, exchanges, bridges, blockchain analytics firms, DeFi services, and other virtual asset service providers to block transactions with or derived from addresses TraderTraitor actors are using to launder the stolen assets.」(FBI 鼓勵私營部門實體,包括 RPC 節點營運商、交易所、跨鏈橋、區塊鏈分析公司、DeFi 服務及其他虛擬資產服務提供者,封鎖與 TraderTraitor 行為者用來洗白被盜資產的地址之間的交易,以及源自這些地址的交易。)
第二步:換個形態
TRM Labs 在 3 月 3 日寫道:「All of the stolen ETH has now been moved to new addresses, with the vast majority bridged to Bitcoin, mostly via services using THORchain.」(所有被盜的 ETH 現在都已轉移到新地址,其中絕大部分已跨鏈換成比特幣,主要透過使用 THORchain 的服務。)Elliptic 補上了時間線:這 50 個錢包「were then emptied one by one over the next nine days. The last of the original 50 wallets holding the stolen funds was emptied on 3rd March.」(在隨後九天裡被逐一清空。最初存放被盜資金的 50 個錢包中,最後一個在 3 月 3 日被清空。)
第三步:隱入暗處
TRM:「We have now entered that second phase and have seen an initial tranche of Bybit's BTC being deposited to mixers including Wasabi and CryptoMixer.」(我們現在已進入第二階段,並看到第一批來自 Bybit 的 BTC 被存入 Wasabi 和 CryptoMixer 等混幣器。)Elliptic:「this bitcoin has now begun to be passed through mixers, to further obfuscate the transaction trail.」(這些比特幣現已開始經過混幣器,以進一步掩蓋交易軌跡。)
而且,這筆錢和更早的錢匯到了一起。Chainalysis:「Funds from the Bybit exploit have also consolidated in addresses holding funds from other known DPRK-linked attacks, providing further evidence that the nation state actors are behind this latest incident.」(來自 Bybit 攻擊的資金也匯集到了存有其他已知北韓相關攻擊資金的地址中,進一步證明這次事件的幕後是國家級行為者。)
然後是兌現,以及這些錢用來做什麼
最後一步是把加密貨幣換成能花的錢。聯合國專家小組列出的模式之一是:「Heavy reliance on third party launderers and over-the-counter brokers」(嚴重依賴第三方洗錢者和場外經紀商)。美國財政部也制裁了「a PRC-based OTC virtual currency trader who facilitated the conversion of virtual currency stolen by DPRK actors working with the Lazarus Group to fiat currency.」(一名以中國為據點的場外虛擬貨幣交易商,他協助與 Lazarus Group 合作的北韓行為者把盜來的虛擬貨幣兌換成法定貨幣。)
用來做什麼?同一份聯合國報告寫道:「A second Member State reported that 40 per cent of the weapons of mass destruction programmes … are funded by illicit cybermeans.」(另一會員國報告稱,40% 的大規模毀滅性武器計畫……由非法網路手段提供資金。)這是某一個國家向專家小組提供的數字,不是專家小組自己的結論。
通常是怎麼開始的
不是從程式碼開始,而是從一則訊息開始。CISA:「The messages often mimic a recruitment effort and offer high-paying jobs to entice the recipients to download malware-laced cryptocurrency applications」(這些訊息常常偽裝成招募,以高薪職位引誘收件人下載夾帶惡意軟體的加密貨幣應用程式)。FBI 列出的警示信號之一:「Requests to conduct a 'pre-employment test' or debugging exercise that involves executing … scripts, or GitHub repositories.」(要求進行「到職前測驗」或除錯練習,其中需要執行……腳本或 GitHub 儲存庫。)
- 不要執行陌生人傳給你的程式碼,哪怕工作機會再誘人。
- 簽署之前,在裝置本身上核對交易內容,而不是看發出請求的那個網頁。
來源
- FBI IC3,North Korea Responsible for $1.5 Billion Bybit Hack,2025 年 2 月 26 日
- Elliptic,The largest theft in history: following the money trail from the Bybit hack,2025 年 2–3 月
- TRM Labs,Bybit hack update: North Korea moves to next stage of laundering,2025 年 3 月 3 日
- Chainalysis,Collaboration in the wake of record-breaking Bybit theft,2025 年 2 月 24 日
- Chainalysis,New OFAC sanctions and DOJ complaint for North Korea-linked cryptocurrency laundering scheme,2020 年 3 月 5 日
- Money Laundering Watch,Two Chinese nationals charged with laundering over $100 million in cryptocurrency for North Korea,2020 年 3 月 11 日
- Sygnia,Sygnia's investigation into the Bybit hack
- 聯合國專家小組(UN Panel of Experts),S/2024/215,2024 年 3 月 7 日
- 美國財政部(US Treasury),jy1435,2023 年 4 月 24 日
- CISA,AA22-108A: TraderTraitor;FBI,PSA 240903,2024 年 9 月 3 日
影片以程式碼製作動畫,腳本在 AI 協助下撰寫;上面每段引文都對照出處查證過,51 個地址這個數字是我們自己數的。示意的部分:錢包地址、每一跳的金額、剝離鏈、螢幕畫面和訊息。本文只在 FBI 和分析機構描述的層面解釋這次洗錢,並不教人怎麼做。影片用 Shotloop 製作:我做的免費 Mac 應用程式,用程式碼做科普短片,一個鏡頭一個鏡頭地修改。