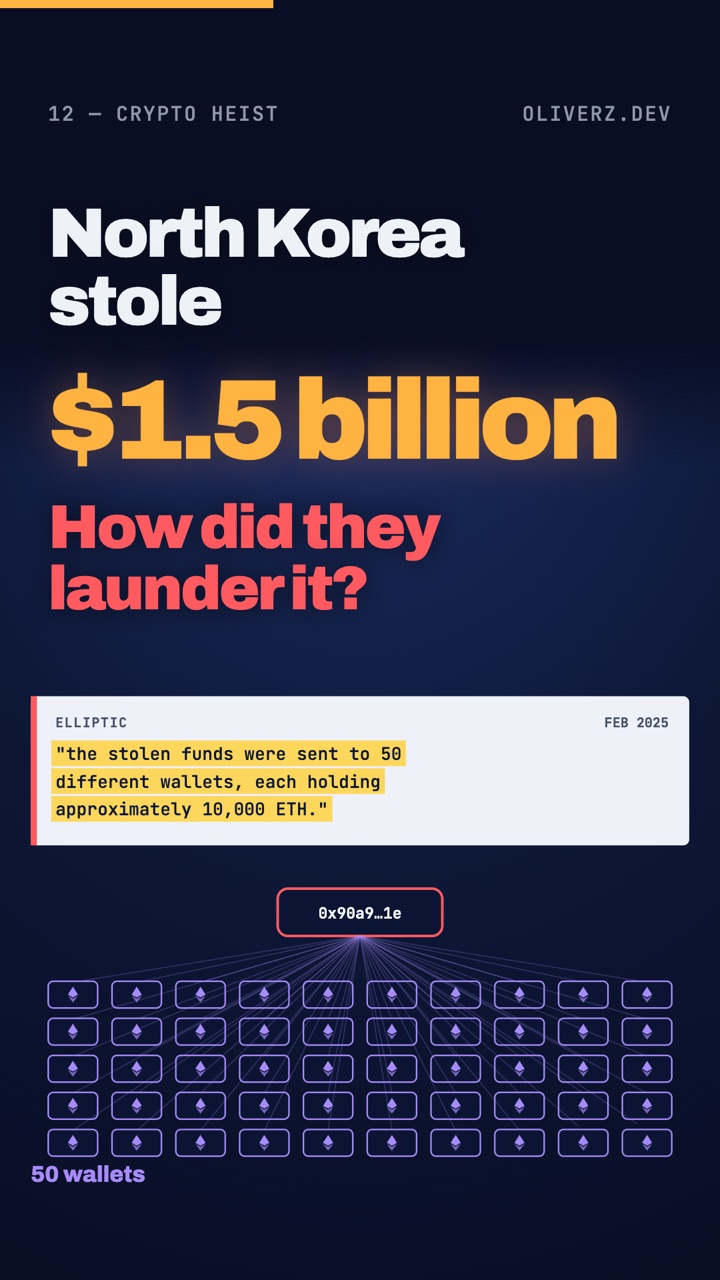
요약: 2025년 2월 21일, FBI가 북한 소행으로 지목한 해커들이 거래 한 건으로 거래소 Bybit에서 약 401,000 이더, 약 15억 달러를 가져갔습니다. 세탁은 세 단계로 이뤄졌습니다. 쪼개기: 두 시간 안에 이더는 지갑 50개에 나뉘어 담겼고, 이어 점점 더 많은 주소로 옮겨 갔습니다. Lazarus가 예전에도 써 온 필 체인(peel chain) 방식입니다. 형태 바꾸기: 스왑 서비스, 대부분 THORChain을 쓰는 서비스를 거쳐 이더는 비트코인이 됐고, 9일 만에 지갑 50개가 모두 비었습니다. 어둠 속으로: 믹서를 거친 뒤, 이전 북한 해킹의 장물을 이미 담고 있던 주소로 들어갔습니다. 5일째에 FBI는 북한을 지목하고, 거래소와 브리지에 해당 주소를 차단해 달라고 요청했습니다.
도난: 거래 한 건
FBI: "North Korea was responsible for the theft of approximately $1.5 billion USD in virtual assets from cryptocurrency exchange, Bybit, on or about February 21, 2025."(북한은 2025년 2월 21일경 암호화폐 거래소 Bybit에서 약 15억 달러 상당의 가상자산을 탈취한 책임이 있다). Chainalysis는 이를 "approximately 401,000 ETH"(약 401,000 ETH)로 봅니다.
침입 경로는 Bybit가 쓰던 다중 서명 서비스 Safe{Wallet}이었습니다. Sygnia는 "a macOS workstation belonging to a Safe{Wallet} developer… was compromised on February 4, 2025"(Safe{Wallet} 개발자의 macOS 워크스테이션이… 2025년 2월 4일에 침해됐다)는 사실과, Safe의 웹 인터페이스에 심어진 코드에 "an activation condition, set to execute the transaction manipulation only on a specific Bybit's cold wallet"(특정 Bybit 콜드 월렛에서만 거래 조작을 실행하도록 설정된 활성화 조건)이 있었다는 사실을 밝혀냈습니다. 그래서 "the Safe{Wallet} user interface displayed legitimate transaction data while malicious transactions were signed and executed."(Safe{Wallet} 사용자 인터페이스에는 정상 거래 데이터가 표시되는 동안 악성 거래가 서명되고 실행됐다).
1단계: 쪼개고, 벗겨 내기
Elliptic: "Within two hours of the theft, the stolen funds were sent to 50 different wallets, each holding approximately 10,000 ETH."(도난 후 두 시간 안에 탈취된 자금은 각각 약 10,000 ETH를 담은 서로 다른 지갑 50개로 보내졌다).
그다음 흔적은 더 길어집니다. 필 체인을, 미국 법무부 소장을 요약한 2020년 글은 이렇게 설명합니다: "a single address begins with a relatively large amount of cryptocurrency. A smaller amount is then "peeled" off this larger amount… and the remainder is transferred to a one-time change address. This process is repeated – potentially hundreds or thousands of times"(하나의 주소가 비교적 큰 금액의 암호화폐로 시작한다. 그 큰 금액에서 더 작은 금액을 '벗겨 내고'… 나머지는 일회용 잔돈 주소로 옮긴다. 이 과정이 반복된다. 수백, 수천 번에 이를 수도 있다). Lazarus의 오래된 방식입니다. 그 2020년 사건에 대한 Chainalysis의 설명: "Lazarus collaborated with Tian and Li to launder the stolen cryptocurrency, conducting hundreds of transactions and forming peel chains that further obfuscated the path of funds."(Lazarus는 Tian, Li와 협력해 탈취한 암호화폐를 세탁했으며, 수백 건의 거래를 실행하고 필 체인을 만들어 자금 경로를 더욱 흐렸다).
Bybit 자금에서 필 체인을 구체적으로 추적한 출처는 아직 보지 못했습니다. 그래서 영상 속 체인은 설명을 위한 연출입니다. FBI가 실제로 밝힌 것은 탈취 자산이 "dispersed across thousands of addresses on multiple blockchains."(여러 블록체인의 수천 개 주소로 흩어졌다)는 것입니다.
5일째: FBI
2월 26일, FBI는 북한을 지목하고("FBI refers to this specific North Korean malicious cyber activity as "TraderTraitor""(FBI는 이 특정한 북한의 악성 사이버 활동을 'TraderTraitor'라고 부른다)) 주소 목록을 공개했습니다: "The following Ethereum addresses are holding or have held assets from the theft, and are operated by or closely connected to North Korean TraderTraitor actors"(다음 이더리움 주소들은 이번 도난 자산을 보유하고 있거나 보유했던 주소로, 북한 TraderTraitor 행위자가 운영하거나 그들과 밀접하게 연결돼 있다). 저희가 세어 보니 51개입니다. 공지 자체에는 개수가 나와 있지 않습니다.
FBI의 요청: "FBI encourages private sector entities including RPC node operators, exchanges, bridges, blockchain analytics firms, DeFi services, and other virtual asset service providers to block transactions with or derived from addresses TraderTraitor actors are using to launder the stolen assets."(FBI는 RPC 노드 운영자, 거래소, 브리지, 블록체인 분석 업체, DeFi 서비스 및 기타 가상자산 서비스 제공자를 비롯한 민간 부문에, TraderTraitor 행위자가 탈취 자산 세탁에 쓰고 있는 주소와의 거래나 그 주소에서 파생된 거래를 차단할 것을 권고한다).
2단계: 형태 바꾸기
TRM Labs, 3월 3일: "All of the stolen ETH has now been moved to new addresses, with the vast majority bridged to Bitcoin, mostly via services using THORchain."(탈취된 ETH는 이제 모두 새 주소로 옮겨졌고, 대부분이 비트코인으로 브리지됐으며, 주로 THORchain을 쓰는 서비스를 거쳤다). Elliptic은 시간표를 보탭니다. 지갑 50개는 "were then emptied one by one over the next nine days. The last of the original 50 wallets holding the stolen funds was emptied on 3rd March."(이후 9일에 걸쳐 하나씩 비워졌다. 탈취 자금을 담은 원래 지갑 50개 중 마지막 지갑은 3월 3일에 비워졌다).
3단계: 어둠 속으로
TRM: "We have now entered that second phase and have seen an initial tranche of Bybit's BTC being deposited to mixers including Wasabi and CryptoMixer."(이제 그 두 번째 단계에 들어섰으며, Bybit의 BTC 첫 물량이 Wasabi와 CryptoMixer를 비롯한 믹서에 입금되는 것을 확인했다). Elliptic: "this bitcoin has now begun to be passed through mixers, to further obfuscate the transaction trail."(이 비트코인은 이제 거래 흔적을 더 흐리기 위해 믹서를 거치기 시작했다).
그리고 이 돈은 예전 돈과 합쳐졌습니다. Chainalysis: "Funds from the Bybit exploit have also consolidated in addresses holding funds from other known DPRK-linked attacks, providing further evidence that the nation state actors are behind this latest incident."(Bybit 공격 자금은 북한과 연관된 것으로 알려진 다른 공격의 자금을 담은 주소로도 모였으며, 이는 이번 사건의 배후가 국가 행위자라는 추가 증거가 된다).
그다음은 현금, 그리고 그 돈이 쓰이는 곳
마지막 단계는 암호화폐를 쓸 수 있는 돈으로 바꾸는 일입니다. 유엔 전문가 패널이 꼽은 패턴 가운데 하나: "Heavy reliance on third party launderers and over-the-counter brokers"(제3자 세탁업자와 장외(OTC) 중개인에 대한 높은 의존). 그리고 미국 재무부는 "a PRC-based OTC virtual currency trader who facilitated the conversion of virtual currency stolen by DPRK actors working with the Lazarus Group to fiat currency."(Lazarus 그룹과 함께 활동하는 북한 행위자들이 훔친 가상화폐를 법정화폐로 바꾸는 일을 도운 중국 기반 OTC 가상화폐 거래인)을 제재했습니다.
무엇을 위해서일까요? 같은 유엔 보고서: "A second Member State reported that 40 per cent of the weapons of mass destruction programmes … are funded by illicit cybermeans."(또 다른 회원국은 대량살상무기 프로그램의 40%가 … 불법적인 사이버 수단으로 자금을 조달한다고 보고했다). 이는 한 나라가 패널에 제출한 수치이며, 패널 자체의 결론이 아닙니다.
보통은 이렇게 시작된다
코드가 아니라 메시지로 시작됩니다. CISA: "The messages often mimic a recruitment effort and offer high-paying jobs to entice the recipients to download malware-laced cryptocurrency applications"(이 메시지들은 흔히 채용 제안을 흉내 내고 고액 연봉 일자리를 내세워, 받는 사람이 악성코드가 심긴 암호화폐 애플리케이션을 내려받도록 유인한다). FBI가 꼽은 경고 신호 가운데 하나: "Requests to conduct a 'pre-employment test' or debugging exercise that involves executing … scripts, or GitHub repositories."(… 스크립트나 GitHub 저장소를 실행해야 하는 '입사 전 테스트'나 디버깅 과제를 요구하는 것).
- 낯선 사람이 보낸 코드는 실행하지 마세요. 일자리 제안이 아무리 좋아도요.
- 서명하기 전에, 서명을 요청한 웹페이지가 아니라 기기 자체에서 거래 내용을 읽으세요.
출처
- FBI IC3, North Korea Responsible for $1.5 Billion Bybit Hack, 2025년 2월 26일
- Elliptic, The largest theft in history: following the money trail from the Bybit hack, 2025년 2~3월
- TRM Labs, Bybit hack update: North Korea moves to next stage of laundering, 2025년 3월 3일
- Chainalysis, Collaboration in the wake of record-breaking Bybit theft, 2025년 2월 24일
- Chainalysis, New OFAC sanctions and DOJ complaint for North Korea-linked cryptocurrency laundering scheme, 2020년 3월 5일
- Money Laundering Watch, Two Chinese nationals charged with laundering over $100 million in cryptocurrency for North Korea, 2020년 3월 11일
- Sygnia, Sygnia's investigation into the Bybit hack
- UN Panel of Experts, S/2024/215, 2024년 3월 7일
- US Treasury, jy1435, 2023년 4월 24일
- CISA, AA22-108A: TraderTraitor; FBI, PSA 240903, 2024년 9월 3일
영상은 코드로 애니메이션을 만들었고, 대본은 AI의 도움을 받아 썼습니다. 위의 모든 인용은 원문과 대조해 확인했으며, 주소 51개라는 개수는 저희가 직접 센 것입니다. 설명을 위한 연출: 지갑 주소, 단계별 금액, 필 체인, 화면과 메시지. 이 글은 FBI와 분석 업체들이 설명하는 수준에서 세탁 과정을 설명할 뿐, 그 방법을 알려 주지 않습니다. 영상은 Shotloop으로 만들었습니다. 코드로 설명 영상을 만들고 한 샷씩 고칠 수 있는 제가 만든 무료 Mac 앱입니다.